- Start setting up the integration in Encord.
- Configure Workload Identity Federation in your GCP project.
- Set up a CORS configuration.
Ensure all objects in the bucket use the Standard Storage class.
1. Start Setting Up The Integration
- Navigate to Workspace Settings > Cloud Buckets and click +New integration.
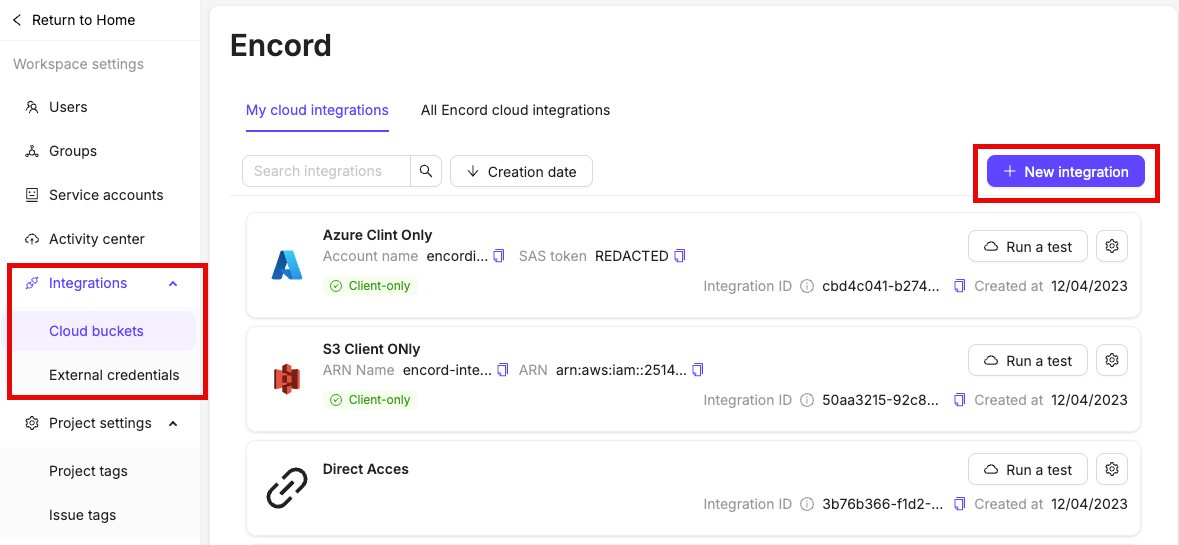
- Select Google Cloud Storage.
- Give your integration a meaningful title.
- Select Workload Identity Federation (WIF).

- Under Choose authentication type, select either Encord service account to follow the steps below, or Workload Identity Federation (WIF) to use short-lived tokens without sharing credentials.
Use Workload Identity Federation
To use WIF, a Workspace admin must first go to Workspace Organization settings > Service integrations, click New service integration, enter a title, set Used for to GCP, and click Create service integration. After selecting Workload Identity Federation (WIF) in the GCP integration form:- Select the GCP service integration that signs the tokens.
- Enable the IAM, Security Token Service, and IAM Service Account Credentials APIs. The form links to each API.
- Create a workload identity pool and add an OpenID Connect (OIDC) provider. Copy the issuer, attribute mapping, and attribute condition displayed by Encord into the provider configuration.
- Paste the provider’s full resource name into Encord. Use the project number, not the project ID, and omit the
https://iam.googleapis.com/prefix. - Create a Google Cloud service account and grant it Storage Object Viewer on the bucket. Grant Storage Object Creator as well if Encord needs to write to the bucket.
- Paste the service account email into Encord, then grant Service Account Token Creator to the principal displayed in the form.
2. Configure Workload Identity Federation
The integration form provides the values you need for the following steps:- Select an Encord service integration that has Used for set to GCP. If none is available, create one from the Service integrations page, then return to the integration form.
- Enable the IAM API, Security Token Service API, and IAM Service Account Credentials API in your GCP project.
- In Google Cloud, go to IAM & Admin > Workload Identity Federation and create a workload identity pool.
- Add a provider to the pool using the settings shown in the Encord integration form:
- Provider type: OpenID Connect (OIDC)
- Provider name / ID:
encord - Issuer (URL): Copy the displayed issuer URL.
- JWK file: Leave empty so Google fetches the keys from the issuer.
- Audiences: Default audience
- Attribute mapping:
google.subject = assertion.sub - Attribute conditions: Copy the displayed
assertion.sub == 'service-integration:<SERVICE_INTEGRATION_UUID>'condition.
- Copy the provider’s resource name from Google Cloud into Encord. Use the project number, not the project ID, and omit the
https://iam.googleapis.com/prefix. The resource name has this format:
- Create a Google Cloud service account and grant it access to your bucket. Assign
Storage Object Viewerfor read access andStorage Object Creatorif you use features that write to the bucket, including re-encoding data and creating image sequences. Paste the service account email into Encord. - On the service account’s Permissions tab, grant the Service Account Token Creator role to the principal shown in the Encord integration form.
Workload Identity Federation uses short-lived credentials. You do not need to create or share a service account key.
3. Create a CORS Configuration
A CORS configuration must be applied to the bucket you want to integrate with Encord. A CORS configuration enables Encord to request resources from the specified bucket.The only way to create a CORS configuration is using the command line or terminal tool.
gcloud command in your command line or terminal to create a CORS configuration.
- Replace <YOUR_BUCKET_NAME> with the name of the bucket you want to integrate.
- Replace
/path/to/you/cors.jsonwith the full path to your JSON CORS file. A sample JSON file is provided below.
JSON configuration file
The following JSON file can be used to set up the CORS configuration in Step 4 of your GCP integration.- Preflight requests are valid for 1 hour. Use the
maxAgeSecondsvariable to adjust the number of seconds the browser is allowed to make requests before it must repeat the preflight request. - Successful browser requests return the
Content-Typeof the resource in the response, as set by theresponseHeader. - Byte-range requests (
GET/HEAD) require theRangerequest header and the exposed response headers shown above so large scene files (such as MCAP) can stream in chunks in the browser.
4. Test Integration
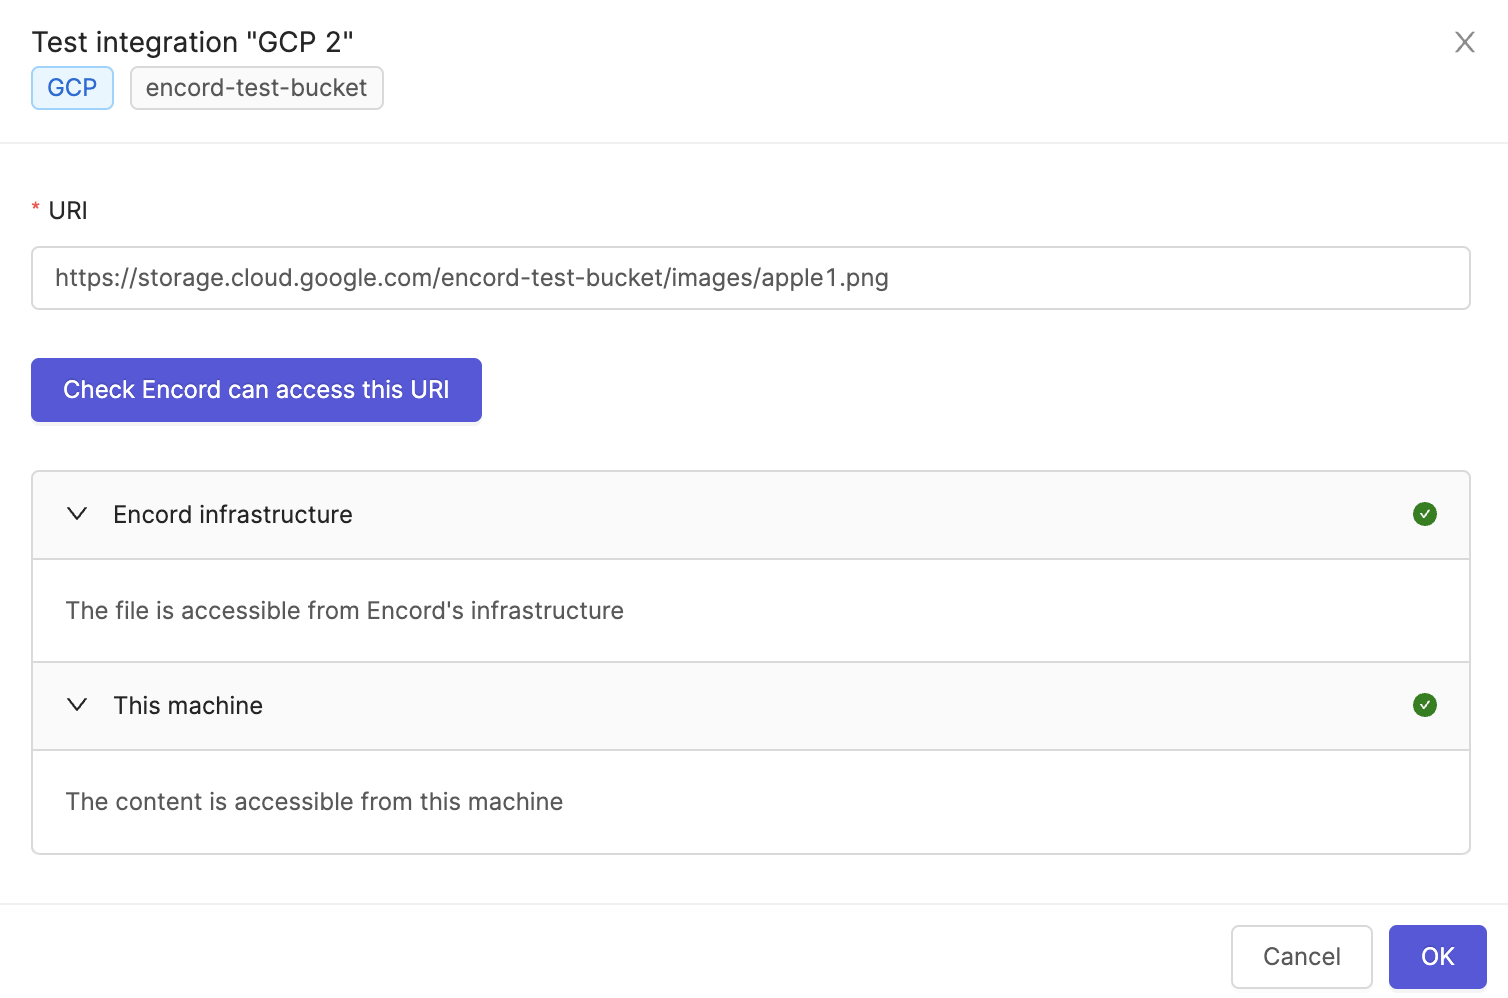
Click the Run a test button on the integration to test the integration.